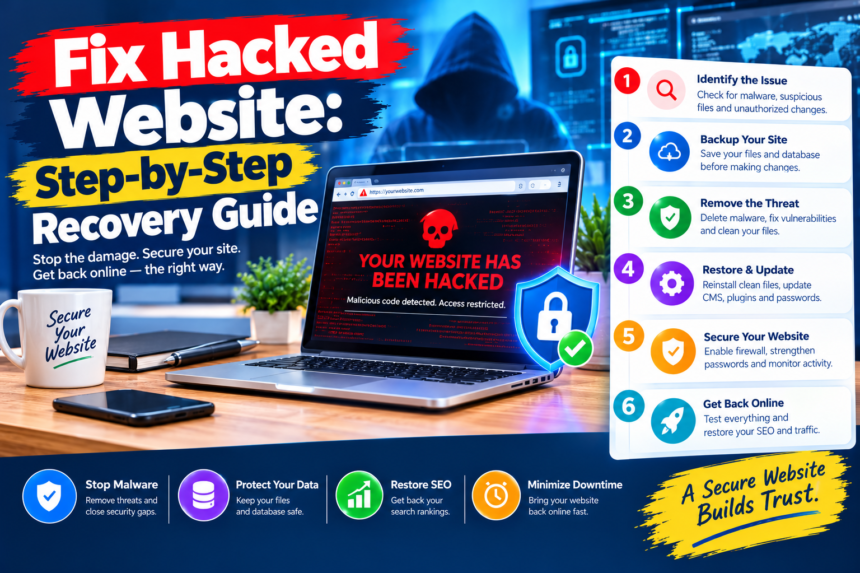
A website hack is a digital nightmare. One moment your site is thriving, the next it’s defaced, redirecting users to spam, or worse, serving malware. The immediate reaction is often panic, but a systematic, step-by-step approach is crucial to not only recover your site but also prevent future attacks. This comprehensive guide will walk you through the entire process to fix hacked website issues, from immediate damage control to long-term security hardening, ensuring your digital presence is restored and fortified.
Phase 1: Immediate Response & Damage Control to Fix Hacked Website Issues
When you discover your website has been compromised, every second counts. Your first actions are critical to minimize damage, prevent further spread, and gather evidence.
Confirming the Hack
Before you do anything drastic, confirm that your site is indeed hacked. Signs can range from obvious to subtle:
- Defacement: Your homepage or other pages are replaced with a hacker’s message or malicious content.
- Spam Content/Links: New, unauthorized pages or links appear on your site, often related to pharmaceuticals, gambling, or adult content.
- Redirects: Visitors are automatically redirected to other, often malicious, websites.
- Search Engine Warnings: Google or other search engines might flag your site as “This site may be hacked” or “This site may harm your computer.”
- Login Issues: You can’t log into your admin panel, or new, unauthorized admin users appear.
- Performance Degradation: Your site is unusually slow, crashes frequently, or consumes excessive server resources.
- Suspicious Files: You find unfamiliar files or folders via FTP/SFTP or your hosting file manager.
- Email Spam: Your website’s email accounts are sending out spam.
- Security Scans: A security scanner (e.g., Sucuri SiteCheck, Google Safe Browsing) identifies malware.
Recognizing these signs is the first crucial step to effectively fix hacked website problems. Once you’ve confirmed the hack, proceed with urgency.
Isolating the Website
The very first action is to take your site offline or restrict access. This prevents further infection, stops the spread of malware to visitors, and allows you to work on it without active interference from the attacker. This critical step helps to contain the damage and prepare your environment to fix hacked website vulnerabilities without further interference.
- Change DNS Records (Temporary): Point your domain’s A record to an internal IP address (e.g.,
127.0.0.1or0.0.0.0) or a temporary “under maintenance” page hosted elsewhere. This is the most effective way to take it offline quickly. - Disable the Website via Hosting Panel: Most hosting providers offer an option to disable or suspend a website from your control panel (cPanel, Plesk, etc.). This usually stops all web traffic to your site.
- Modify
.htaccess: If you can still access your site’s files, you can temporarily block all traffic by adding rules to your.htaccessfile (located in your site’s root directory). For example, to deny all access:Order deny,allow Deny from allOr, to allow only your IP address:
Order deny,allow Deny from all Allow from your.ip.addressRemember to replace
your.ip.addresswith your actual public IP. You can find your IP by searching “what is my IP” on Google. - Change FTP/SFTP Password: If the attacker gained access via FTP, changing the password immediately cuts off that avenue.
Do not delete anything yet. The goal is isolation, not eradication at this stage.
Changing All Passwords
Assume every password associated with your website has been compromised. Change them immediately, starting with the most critical. This is a non-negotiable step to truly fix hacked website access points.
- Hosting Control Panel (cPanel, Plesk, etc.): This is paramount as it grants access to everything.
- Database Passwords: Update the password for your database user. After changing it in your hosting panel, you’ll need to update your website’s configuration file (e.g.,
wp-config.phpfor WordPress) with the new password. - WordPress Admin (or CMS Admin): Change passwords for all administrator accounts. If new, unauthorized admin accounts exist, do not delete them yet, but change their passwords if possible and make a note.
- FTP/SFTP Accounts: Change passwords for all FTP/SFTP users. Delete any unfamiliar FTP accounts.
- Email Accounts: Change passwords for all email accounts associated with your domain, especially those used for admin purposes or password resets.
- API Keys/External Services: If your site integrates with third-party services (e.g., payment gateways, email marketing, CDN), change those API keys or passwords if they are stored on your server or were accessible.
Use strong, unique passwords for each service. A password manager is highly recommended.
Notifying Your Hosting Provider
Your hosting provider is a critical ally. Contact their support team immediately. They are often equipped to assist you to fix hacked website issues at a server level.
- Report the Incident: Inform them that your website has been hacked.
- Request Assistance: They might have server-side scanners, logs, or even dedicated security teams that can help identify the breach point and clean your site.
- Check for Account Compromise: Ask them to check if your hosting account itself was compromised or if other sites on your shared hosting account (if applicable) are affected.
- Cooperate: Provide them with any information you have, such as when you first noticed the hack, what symptoms you observed, and what steps you’ve already taken.
Some hosts offer malware removal services, often for a fee, but their expertise can be invaluable.
Backing Up the Hacked Site (Crucial for Forensics)
This step might seem counterintuitive – why back up an infected site? This backup is not for restoration but for forensic analysis. It’s a snapshot of the compromised state, which can be invaluable for understanding how the breach occurred and ensuring you’ve found all malicious code. This forensic backup is vital for understanding the attack vector and ensuring you completely fix hacked website compromises.
- Full Backup: Use your hosting provider’s backup tool (cPanel, Plesk) or an FTP client to download all website files and export your database.
- Store Separately: Keep this backup isolated from your clean backups and your working environment. Label it clearly as “Hacked Site Backup – [Date]”.
- Do Not Restore From This Backup: This backup is for analysis only. You will restore from a clean backup later, or manually clean your site.
Having this forensic backup can help you identify hidden backdoors that might otherwise be missed during the cleaning process.
Phase 2: Identification & Eradication
With your site isolated and passwords secured, it’s time to dig in, find the malicious code, and remove it. This is the most labor-intensive phase.
Scanning for Malware and Vulnerabilities
Utilize both server-side and external scanners to get a comprehensive view of the infection. These scans provide a roadmap to effectively fix hacked website infections.
Server-Side Scanners
These tools run on your server or are integrated into your CMS, providing deep analysis of your files and database.
- WordPress Security Plugins (e.g., Wordfence, Sucuri Security, iThemes Security): If you can still access your WordPress admin, install and run one of these plugins. They are designed to scan core files, themes, plugins, and the database for known malware, suspicious code, and unauthorized changes. They can often identify the exact files that are infected.
- Hosting Provider Scanners: Many hosts offer their own malware scanners or integrate with services like Imunify360. Check your hosting control panel for these options.
- Dedicated Malware Removal Services: Companies like Sucuri and SiteLock offer comprehensive scanning and removal services. They often have proprietary tools that can detect even sophisticated malware.
External Scanners
These scan your site from the outside, looking for publicly visible signs of compromise.
- Google Safe Browsing: Check your site’s status at Google Transparency Report.
- Sucuri SiteCheck: A free online scanner that checks your site for malware, blacklisting status, and common vulnerabilities.
- VirusTotal: Upload suspicious files from your site to VirusTotal for analysis by multiple antivirus engines.
- URLVoid: Similar to Sucuri SiteCheck, it checks your URL against various blacklisting services and scanners.
These scans will give you a list of potentially infected files or areas to investigate.
Identifying the Entry Point
Finding how the attacker got in is crucial to prevent a re-infection. This requires detective work. Understanding the entry point is key to not only cleaning the current infection but also preventing future attacks and truly fix hacked website weaknesses.
Access Logs
Your server’s access logs (usually found in your hosting control panel) record every request made to your website. Look for:
- Unusual IP Addresses: IPs from countries you don’t typically receive traffic from, or IPs known for malicious activity.
- Suspicious POST Requests: Look for POST requests to files you don’t recognize, especially in directories like
wp-content/uploadsor temporary folders. Hackers often upload web shells (malicious scripts that give them remote control) via vulnerable forms or outdated plugins. - Repeated Login Attempts: Brute-force attacks will show up as numerous failed login attempts to your admin URL.
Error Logs
Error logs can reveal failed attempts by the attacker or errors caused by their malicious code.
- PHP Errors: Look for errors related to unknown functions, file inclusions, or attempts to execute code from unusual locations.
- Failed Login Attempts: Similar to access logs, these indicate brute-force attacks.
File Modification Dates
This is one of the most effective ways to narrow down the timeframe of the hack.
- FTP/SFTP Client or File Manager: Connect to your site and sort files by “Last Modified Date.”
- Command Line (SSH): If you have SSH access, use commands like
ls -laR --time-style=full-iso | grep "YYYY-MM-DD"to list files modified on specific dates. Focus on files modified around the time you suspect the hack occurred. - Look for: Newly created files in unusual directories (e.g.,
.phpfiles inwp-content/uploads), recently modified core files, or changes to.htaccess.
Common Vulnerabilities
Most hacks exploit known weaknesses. Consider these common entry points:
- Outdated Software:
- WordPress Core: If your WordPress version is old, it likely has known security vulnerabilities.
- Plugins and Themes: These are the most common entry points. Outdated or poorly coded plugins/themes often have exploitable flaws.
- PHP Version: Running an old PHP version (e.g., PHP 5.x) can expose your site to vulnerabilities and compatibility issues.
- Weak Passwords: Easily guessable passwords for admin accounts, FTP, or database.
- Insecure File Permissions: Files or directories with
777permissions are highly risky, allowing anyone to write to them. - Lack of Web Application Firewall (WAF): A WAF can block many common attack vectors before they reach your site.
Pinpointing the entry point helps you understand the scope of the damage and prevent future attacks.
Cleaning the Malware to Fix Your Hacked Website
This is where you remove all traces of the infection. There are two primary approaches: restoring from a clean backup or manual cleaning.
Restoring from a Clean Backup (Ideal Scenario)
If you have a backup from before the hack occurred and you are certain it’s clean, this is the fastest and safest method. This is often the quickest and most reliable way to fix hacked website problems.
- Verify Backup Integrity: Ensure the backup is truly clean. Scan it locally if possible.
- Delete All Current Files: Completely wipe your website’s files from your server (after making your forensic backup!).
- Drop Database Tables: Delete all tables in your database (after exporting your forensic database backup!).
- Restore Backup: Upload the clean files and import the clean database.
- Change Passwords Again: Even after restoring, change all critical passwords (hosting, database, admin, FTP) one more time, just to be safe.
- Immediately Update Everything: Once restored, update WordPress core, all plugins, and themes to their latest versions.
- Scan Again: Run a full security scan to confirm the site is clean.
Manual Cleaning (If No Clean Backup or for Forensics)
If you don’t have a clean backup, or if you want to understand the hack deeply, manual cleaning is necessary. This is complex and requires technical expertise. Manual cleaning is a meticulous process, but it allows for a deep understanding of the breach and a thorough approach to fix hacked website vulnerabilities.
- Re-upload WordPress Core Files:
- Download a fresh copy of your exact WordPress version from wordpress.org/download/releases/.
- Delete all existing WordPress core files and directories except for
wp-config.phpand thewp-contentdirectory. - Upload the fresh core files.
- Crucial: Compare your
wp-config.phpwith a fresh one. Look for any added malicious code. Only keep your database credentials, salts, and any legitimate custom configurations.
- Clean Plugins and Themes:
- Delete All: The safest approach is to delete all plugins and themes from your site.
- Reinstall from Trusted Sources: Download fresh copies of all your required plugins and themes from the official WordPress plugin directory or their original vendors.
- Avoid Nulled/Pirated Versions: These are often pre-infected.
- Review Code (if necessary): If you suspect a specific plugin/theme was the entry point, you might need to manually inspect its files for malicious code.
- Database Cleaning:
- Access your database via phpMyAdmin or a similar tool.
- Look for:
- New Admin Users: Check the
wp_userstable for any unauthorized user accounts. Delete them. - Injected Spam: Search
wp_postsandwp_optionstables for spam links, keywords, or obfuscated code. Common targets aresiteurl,home,blogdescription,blognameinwp_options. - Malicious Scripts: Look for
base64_decode,eval,gzinflate,str_rot13functions inwp_posts(post content) orwp_options(various settings).
- New Admin Users: Check the
- Example SQL Query for
wp_options:SELECT FROM wp_options WHERE option_value LIKE '%base64_decode%'; - Example SQL Query for
wp_posts:SELECT FROM wp_posts WHERE post_content LIKE '%<script%'; - Be extremely careful when modifying the database. Make a backup before making any changes.
- User Accounts:
- Go to your WordPress admin panel (if accessible) and review all user accounts.
- Delete any unfamiliar users.
- Change passwords for all legitimate users, especially administrators.
- Ensure no users have elevated privileges they shouldn’t have.
wp-config.phpand.htaccessFiles:- These files are frequent targets for hackers.
wp-config.php: Compare it with a freshwp-config-sample.phpfrom a new WordPress installation. Look for any added code, especially at the top or bottom, or within existing definitions..htaccess: This file can contain powerful redirect rules. Look forRewriteRuleorRedirectdirectives that you didn’t add, especially those pointing to external domains or suspicious files. A common tactic is to add malicious rules at the very top or bottom of the file. You can often replace it with a fresh.htaccessfile from a new WordPress installation, then re-add any legitimate custom rules you had.
- Other Suspicious Files:
- Web Shells: Look for files with names like
shell.php,cmd.php,r57.php,c99.php, or files with obfuscated names (e.g.,kjhgf.php). These are often found inwp-content/uploads,wp-includes, or the root directory. - Hidden Files: Look for files starting with a dot (e.g.,
.cache,.config) that are not standard. - Unusual Extensions: Files with double extensions (e.g.,
image.jpg.php). - Obfuscated Code: Files containing
eval(base64_decode(...))or similar functions are highly suspicious. - Empty Files with Malicious Content: Sometimes hackers create seemingly empty files that actually contain malicious code. Check file sizes.
- Web Shells: Look for files with names like
Carefully reviewing and cleaning these files is paramount to completely fix hacked website backdoors. This manual cleaning process is meticulous. If you’re unsure, consider hiring a professional.
Phase 3: Hardening & Prevention to Permanently Fix Hacked Website Vulnerabilities
Cleaning the hack is only half the battle. Without proper hardening, your site remains vulnerable to future attacks. Implementing robust security measures is crucial to prevent recurrence and maintain a secure online presence.
Regular Updates & Patching
One of the most common reasons websites get hacked is outdated software. To truly fix hacked website security, you must commit to a rigorous update schedule. Regularly updating your CMS (WordPress, Joomla, Drupal, etc.), all plugins, themes, and your server’s PHP version is a fundamental step to fix hacked website vulnerabilities and maintain a secure environment. These updates often include critical security patches that close known loopholes exploited by attackers. Prioritizing these updates is key to proactively addressing issues and helping to fix hacked website problems before they escalate.
Strong Passwords & Multi-Factor Authentication (MFA)
Weak passwords are an open invitation for attackers. To effectively fix hacked website access issues and prevent brute-force attacks, implement strict password policies. Use long, complex, and unique passwords for all accounts (admin, FTP, database, hosting panel). Furthermore, enable Multi-Factor Authentication (MFA) wherever possible. MFA adds an extra layer of security, requiring a second verification step (like a code from your phone) even if your password is compromised. This proactive approach is vital to fix hacked website vulnerabilities related to unauthorized access.
Web Application Firewall (WAF) & Content Delivery Network (CDN)
A WAF acts as a shield between your website and malicious traffic, filtering out common attack vectors like SQL injection, cross-site scripting (XSS), and brute-force attempts. Implementing a WAF is a proactive measure to fix hacked website attempts before they even reach your server. Services like Cloudflare or Sucuri offer WAF capabilities, often bundled with a Content Delivery Network (CDN). A CDN not only improves site speed but can also absorb some DDoS attacks and hide your server’s true IP address, adding another layer of defense. These tools are indispensable for those looking to effectively fix hacked website security at the network edge.
Regular & Off-site Backups
Even with the best security, a hack can still occur. Your ultimate safety net to fix hacked website disasters is a robust backup strategy. Implement automated, regular backups of both your website files and database. Crucially, store these backups off-site, separate from your hosting server. This ensures that even if your entire hosting account is compromised, you have a clean, accessible copy to restore from. A reliable backup is often the quickest way to fix hacked website issues after a major breach.
File Integrity Monitoring (FIM)
FIM tools continuously monitor your website files for unauthorized changes. If a file is modified, added, or deleted without permission, the system alerts you immediately. This is crucial to quickly detect and fix hacked website modifications before they escalate, helping you catch hidden backdoors or new malware injections. Such monitoring is a proactive step to fix hacked website vulnerabilities that might otherwise go unnoticed.
Security Headers
Implementing HTTP security headers can significantly enhance your website’s defense against various attacks. Headers like Content Security Policy (CSP), X-XSS-Protection, X-Content-Type-Options, and Strict-Transport-Security (HSTS) instruct browsers on how to behave when interacting with your site, mitigating risks like XSS and clickjacking. This is a technical but effective way to fix hacked website vulnerabilities at the browser level, preventing client-side exploits.
Principle of Least Privilege
Granting users and applications only the minimum necessary permissions is a core security principle. For example, your WordPress database user should only have permissions to select, insert, update, and delete data, not to create or drop tables. Similarly, limit administrator accounts and assign editor or contributor roles to users who don’t need full control. Applying this helps to limit the damage if an account is compromised, making it easier to fix hacked website breaches. This principle is fundamental to minimizing the attack surface and making it harder for attackers to fix hacked website security by exploiting over-privileged accounts.
Monitoring & Logging
Continuous monitoring of your website’s activity and server logs is essential for early detection of suspicious behavior. Implement log analysis tools or services that can alert you to unusual login patterns, excessive failed attempts, or access to sensitive files. Proactive monitoring helps you to quickly identify and fix hacked website attempts, often before they cause significant damage. Effective logging is a cornerstone for understanding and resolving issues, helping you to fix hacked website problems efficiently.
DDoS Protection
Distributed Denial of Service (DDoS) attacks can take your site offline by overwhelming it with traffic. While not directly related to malware, it’s a form of attack that needs prevention. Services like Cloudflare can help protect against these, ensuring your efforts to fix hacked website security aren’t undermined by availability issues. Implementing DDoS protection is another layer of defense to fix hacked website availability concerns. For a broader look at how technology is shaping security, consider how AI Enhances Cybersecurity in Web3, offering advanced defenses against evolving threats.
Regular Security Audits
Consider engaging professional security auditors to regularly assess your website’s vulnerabilities. Their expertise can uncover hidden weaknesses, misconfigurations, or zero-day exploits that automated scanners might miss. They can provide comprehensive reports and recommendations to proactively fix hacked website risks and strengthen your overall security posture. Regular audits are a critical investment to fix hacked website vulnerabilities before they are exploited.
Educating Users
Human error is often a significant factor in security breaches. Educating all users with access to your website (admins, content creators, etc.) on security best practices is vital to prevent future incidents and help them understand how to avoid actions that could lead to needing to fix hacked website problems. Topics should include strong password creation, recognizing phishing attempts, safe browsing habits, and the importance of reporting suspicious activity. This user awareness is a crucial, often overlooked, step to fix hacked website security gaps.
Successfully recovering from a website hack is a challenging but achievable task. By following this step-by-step guide, you can effectively isolate, identify, clean, and harden your website. Remember, the journey to fix hacked website issues doesn’t end with recovery; it’s an ongoing commitment to vigilance and proactive security measures. Stay informed, stay updated, and maintain a robust security posture to protect your digital assets. With these strategies, you’ll be well-equipped to fix hacked website situations and prevent future compromises.