In an increasingly digital world, the convenience of online shopping, remote payments, and instant transactions has become an indispensable part of our daily lives. From ordering groceries to booking international flights, the ability to make purchases without physically presenting a credit or debit card offers unparalleled flexibility. However, this very convenience opens the door to a significant and growing threat: Card Not Present fraud.
CNP fraud has eclipsed traditional in-person card fraud as the leading type of payment fraud, posing a substantial risk to merchants, financial institutions, and consumers alike. As e-commerce continues its rapid expansion, understanding the intricacies of CNP fraud – its causes, far-reaching impacts, and robust prevention strategies – is no longer optional, but absolutely critical for anyone involved in digital commerce.
This comprehensive guide will delve deep into the world of CNP fraud, exploring what it is, why it’s on the rise, how fraudsters operate, the severe consequences it entails, and the multi-layered defenses necessary to combat it effectively.
What is Card Not Present fraud?
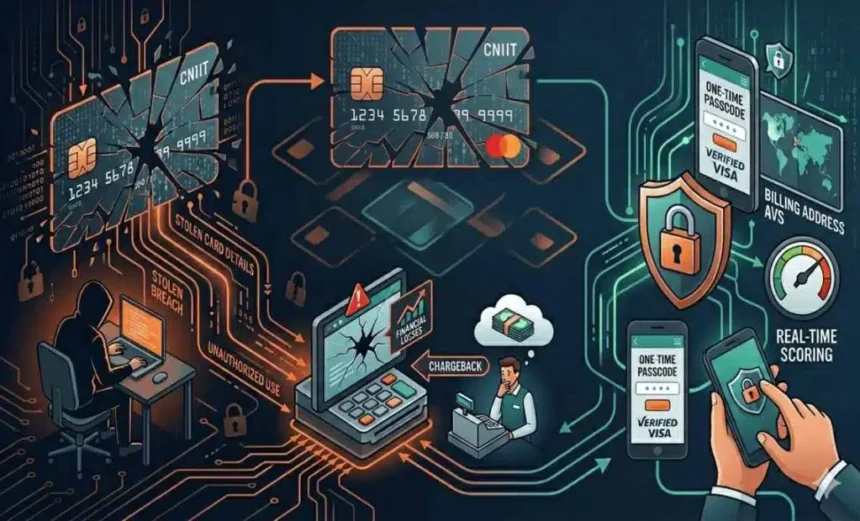
Card Not Present fraud (CNP) fraud refers to a type of credit card fraud where the cardholder does not physically present the payment card to the merchant at the time of the transaction. This means the merchant cannot visually inspect the card for security features or verify the cardholder’s identity through a signature or PIN.
Instead, the transaction relies solely on the card details provided by the customer, such as the card number, expiration date, and Card Verification Value (CVV/CVC).
Common scenarios for CNP transactions include:
- Online Purchases (E-commerce): The most prevalent form, where customers enter their card details on a website or mobile app.
- Mail Order/Telephone Order (MOTO): Transactions initiated over the phone or via mail, where a customer provides card details verbally or in writing.
- Recurring Payments: Subscriptions or bill payments where card details are stored and automatically charged.
- Virtual Terminals: Merchants manually entering card details into a web-based payment system.
CNP Fraud vs. Card Present (CP) Fraud
To better understand CNP fraud, it’s helpful to contrast it with Card Present (CP) fraud:
- Card Present (CP) Fraud: Occurs when a physical card is used fraudulently in person, typically at a point-of-sale (POS) terminal. This type of fraud has significantly decreased in regions that adopted EMV (Europay, MasterCard, and Visa) chip card technology, which encrypts transaction data and makes it nearly impossible to clone a card.
- Card Not Present fraud (CNP) Fraud: Occurs when the card details are stolen and used for transactions where the physical card is not required. Because EMV technology primarily protects in-person transactions, fraudsters have shifted their focus to the less secure CNP environment.
The key vulnerability in CNP transactions is the absence of a physical card and the inability to verify the cardholder’s identity directly. This makes it easier for criminals to use stolen card data without detection, as long as they have the necessary details.
The Rise of CNP Fraud: Why Now?
CNP fraud isn’t a new phenomenon, but its prevalence has surged dramatically in recent years. Several interconnected factors contribute to this alarming trend:
1. The EMV Chip Card Adoption (The “Fraud Shift”)
The widespread adoption of EMV chip cards in many parts of the world, particularly in the United States, has been a double-edged sword. While EMV technology has been highly effective in reducing counterfeit card fraud at physical point-of-sale terminals, it inadvertently pushed fraudsters to exploit the weakest link: the online environment. This phenomenon is often referred to as the “fraud shift” or “liability shift.” With in-person fraud becoming harder, criminals simply migrated their efforts to CNP channels where EMV’s protections don’t apply.
2. The E-commerce Boom
The exponential growth of e-commerce, accelerated further by global events like the COVID-19 pandemic, has created a vast and fertile ground for CNP fraud. More people are shopping online than ever before, leading to an unprecedented volume of CNP transactions. This increased volume makes it harder for merchants and financial institutions to distinguish legitimate transactions from fraudulent ones, providing more opportunities for criminals to slip through the cracks.
3. Proliferation of Data Breaches
High-profile data breaches at major retailers, social media platforms, and financial institutions have become distressingly common. These breaches often expose vast quantities of sensitive customer data, including credit card numbers, expiration dates, CVV codes, names, addresses, and even login credentials. Once this data is stolen, it is often sold on the dark web, making it readily available to fraudsters who then use it to conduct CNP transactions.
4. Sophisticated Fraudster Tactics
Modern fraudsters are highly organized, technologically adept, and constantly evolving their methods. They leverage advanced tools and techniques, including:
- Botnets: Networks of compromised computers used to automate fraud attempts, such as testing stolen card numbers.
- Phishing and Social Engineering: Deceptive tactics to trick individuals into revealing their card details or login credentials.
- Malware and Skimming: Software designed to capture payment information from websites or user devices.
- Account Takeover (ATO): Gaining unauthorized access to legitimate customer accounts to make fraudulent purchases or access stored payment information.
5. Global Reach and Anonymity
The internet offers fraudsters a degree of anonymity and a global reach that traditional fraud methods lacked. Criminals can operate from anywhere in the world, targeting merchants and consumers across borders, making it challenging for law enforcement and financial institutions to track and prosecute them. Cross-border transactions also add complexity to fraud detection and dispute resolution.
6. Inconsistent Security Measures
While many businesses have adopted robust security measures, there remains an inconsistency in implementation across the e-commerce landscape. Smaller businesses, in particular, may lack the resources or expertise to deploy comprehensive fraud prevention tools, making them attractive targets for fraudsters. Even large enterprises can have vulnerabilities that are exploited.
These factors collectively create an environment where CNP fraud can thrive, necessitating a proactive and multi-layered approach to prevention.
How CNP Fraud Works: Common Tactics
Understanding the mechanisms behind CNP fraud is crucial for effective prevention. Fraudsters employ a variety of tactics, often combining several to maximize their success:
1. Phishing and Smishing
- Phishing: Fraudsters send deceptive emails that appear to be from legitimate organizations (banks, popular retailers, government agencies) to trick recipients into revealing sensitive information like credit card numbers, login credentials, or personal data. These emails often contain malicious links that lead to fake websites designed to harvest information.
- Smishing: Similar to phishing, but conducted via SMS text messages. Victims receive texts with urgent-sounding messages (e.g., “Your account has been locked,” “Confirm your package delivery”) containing links to fraudulent sites.
2. Malware and Digital Skimming
- Malware: Malicious software installed on a victim’s computer or mobile device (often through malicious downloads or infected websites) can record keystrokes, capture screenshots, or directly steal payment information as it’s entered.
- Digital Skimming (Magecart Attacks): Fraudsters inject malicious code into legitimate e-commerce websites, typically on the checkout page. This code “skims” payment card details as customers enter them, sending the stolen data directly to the fraudsters. This is analogous to physical card skimmers but operates entirely online.
3. Account Takeover (ATO)
In an ATO attack, fraudsters gain unauthorized access to a legitimate customer’s online account (e.g., on an e-commerce site, airline portal, or loyalty program). They achieve this through:
- Credential Stuffing: Using lists of stolen usernames and passwords (from data breaches) to try and log into accounts on other sites, assuming users reuse credentials.
- Phishing/Social Engineering: Tricking account holders into revealing their login details.
- Once inside, they can update shipping addresses, use stored payment methods, or redeem loyalty points for fraudulent purchases.
4. Brute Force Attacks and Card Testing
- Brute Force Attacks: Fraudsters use automated scripts to systematically guess credit card numbers, expiration dates, and CVV codes. They might start with a known valid card number and try different CVVs or expiration dates.
- Card Testing: To verify if stolen card data is still active and valid, fraudsters often make small, low-value purchases on websites with lax security. If the transaction goes through, they know the card is live and can be used for larger fraudulent purchases. This can lead to numerous small, unauthorized charges on a victim’s statement.
5. Bot Attacks
Sophisticated botnets are deployed to automate various fraud activities:
- Credential Stuffing: As mentioned above, bots can attempt thousands of logins per second.
- Card Testing: Bots can rapidly test stolen card numbers on multiple merchant sites.
- Inventory Hoarding: Bots can quickly purchase limited-edition items to resell at inflated prices, sometimes using stolen cards.
6. Friendly Fraud (Chargeback Fraud)
This type of CNP fraud occurs when a legitimate customer makes a purchase but then disputes the charge with their bank, claiming they never received the goods, the goods were not as described, or they didn’t authorize the transaction, even though the claim is false. While often unintentional (e.g., a family member made a purchase), it can also be intentional and malicious, essentially allowing the customer to receive goods or services for free. This is particularly damaging for merchants as they lose the product, the revenue, and incur chargeback fees.
7. Synthetic Identity Fraud
This advanced form of fraud involves creating a “synthetic” identity by combining real and fake information. Fraudsters might use a real Social Security number (often stolen from a child or someone with a clean credit history) with a fabricated name, address, and date of birth. They then use this synthetic identity to open credit accounts, build a credit history, and eventually make large fraudulent purchases, including CNP transactions, before defaulting. This is harder to detect because it doesn’t match a single real person’s identity.
These tactics highlight the dynamic and persistent nature of CNP fraud, underscoring the need for equally dynamic and robust prevention measures.
Impacts of CNP Fraud: A Multi-faceted Problem
The repercussions of CNP fraud extend far beyond the immediate financial loss of a single transaction. It creates a ripple effect, causing significant damage to merchants, cardholders, and issuing banks.
For Merchants
Merchants bear the brunt of CNP fraud, facing a cascade of financial and operational challenges:
- Financial Losses from Chargebacks: When a cardholder disputes a fraudulent CNP transaction, the merchant is typically held liable. They lose the revenue from the sale, the cost of the goods or services provided, and often incur a chargeback fee (ranging from $20 to $100 per dispute) from their acquiring bank.
- Operational Costs: Managing chargebacks is a labor-intensive process. Merchants must dedicate staff to investigate disputes, gather evidence, and respond to chargeback inquiries, diverting resources from core business activities.
- Lost Goods and Shipping Costs: In cases where physical goods are shipped, merchants lose both the product and the shipping expenses, with no recourse to recover them.
- Increased Processing Fees: A high chargeback ratio can lead to increased transaction processing fees from payment processors. If the ratio exceeds certain thresholds (typically 0.9% to 1.5%), merchants can be placed on fraud monitoring programs, fined, or even have their merchant accounts terminated, making it impossible to process card payments.
- Reputational Damage: Fraudulent transactions and subsequent chargebacks can erode customer trust. If customers perceive a merchant as insecure or difficult to deal with regarding disputes, they may take their business elsewhere.
- PCI DSS Compliance Penalties: While not directly a fraud penalty, if CNP fraud stems from a data breach on a merchant’s system, they could face severe penalties for non-compliance with the Payment Card Industry Data Security Standard (PCI DSS), including fines and audits.
For Cardholders
While cardholders are often protected by “zero liability” policies from their banks, CNP fraud still inflicts stress and inconvenience:
- Temporary Loss of Funds: Even with zero liability, it can take time for banks to investigate and reverse fraudulent charges, temporarily tying up the cardholder’s funds.
- Time and Effort: Cardholders must spend time monitoring their statements, reporting suspicious activity, disputing transactions, and potentially dealing with the hassle of replacing their compromised card.
- Identity Theft Concerns: A CNP fraud incident often signals that personal information has been compromised, leading to anxiety about potential identity theft and the need to take protective measures like credit freezes.
- Loss of Trust: Experiencing fraud can diminish a cardholder’s trust in online merchants and even their own financial institutions.
For Issuing Banks
Issuing banks (the banks that issued the credit or debit card to the cardholder) also face significant impacts:
- Financial Losses: Under zero liability policies, issuing banks are typically responsible for reimbursing cardholders for fraudulent charges. This directly impacts their bottom line.
- Operational Costs: Banks must invest heavily in fraud detection systems, employ fraud analysts, and dedicate resources to investigate and resolve cardholder disputes.
- Reputational Risk: Frequent fraud incidents can damage a bank’s reputation for security and customer protection, potentially leading to customer churn.
- Increased Compliance Burden: Banks must adhere to strict regulatory requirements and industry standards related to fraud prevention and data security.
The interconnected nature of these impacts underscores why CNP fraud is a problem that demands a collaborative and robust prevention strategy across the entire payment ecosystem.
Prevention Strategies: A Multi-Layered Approach
Combating CNP fraud effectively requires a comprehensive, multi-layered strategy that involves technology, processes, and vigilance from all stakeholders. No single solution is foolproof; rather, a combination of tools and best practices offers the strongest defense.
For Merchants
Merchants are on the front lines of CNP fraud prevention and must implement robust measures to protect themselves and their customers.
1. Payment Gateway Security Features
- Address Verification Service (AVS): Checks if the billing address provided by the customer matches the address on file with the card issuer. While not foolproof (as fraudsters may have the correct address from a data breach), it’s a critical first line of defense.
- Card Verification Value (CVV/CVC): Requires customers to enter the 3 or 4-digit security code from the back (or front) of their card. This helps verify that the customer physically possesses the card, as the CVV is not stored in most data breaches.
- 3D Secure (e.g., Verified by Visa, Mastercard SecureCode, American Express SafeKey): An authentication protocol that adds an extra layer of security for online credit and debit card transactions. It typically involves redirecting the customer to their bank’s website to enter a password, a one-time passcode (OTP) sent to their phone, or approve the transaction via their banking app. This shifts liability for fraudulent transactions from the merchant to the issuing bank.
2. Advanced Fraud Detection Tools
- AI and Machine Learning: These systems analyze vast amounts of transaction data in real-time to identify patterns, anomalies, and risk factors that indicate fraud. They can adapt to new fraud tactics, making them highly effective. For a deeper dive into how businesses spot suspicious activity, explore online fraud detection methods.
- Behavioral Analytics: Monitors customer behavior on a website (e.g., typing speed, mouse movements, time spent on pages) to detect deviations from normal patterns that might suggest a bot or a fraudster.
- Transaction Monitoring: Tracks transaction velocity (how many transactions from one card or IP address in a short period), average transaction value, and geographic location to flag suspicious activity.
- IP Geolocation: Identifies the geographical location of the customer’s IP address and compares it to the billing and shipping addresses. A mismatch can be a red flag.
- Device Fingerprinting: Collects non-personally identifiable information about the device being used (operating system, browser, plugins, screen resolution) to create a unique “fingerprint.” This helps identify repeat fraudsters or devices associated with suspicious activity.
- Proxy/VPN Detection: Identifies if a customer is using a proxy server or Virtual Private Network (VPN) to mask their true IP address, which can be a common tactic for fraudsters.
3. Manual Review of High-Risk Transactions
Automated systems are powerful, but some transactions warrant human review. Merchants should set rules to flag transactions for manual inspection, such as:
- Large orders, especially from new customers.
- Orders with different billing and shipping addresses.
- Orders with expedited shipping.
- Multiple orders from the same IP address but different card numbers.
- Orders from high-risk countries.
4. PCI DSS Compliance
Adhering to the Payment Card Industry Data Security Standard (PCI DSS) is fundamental. This set of security standards ensures that all companies that process, store, or transmit credit card information maintain a secure environment, significantly reducing the risk of data breaches that could lead to CNP fraud.
5. Tokenization and Encryption
- Tokenization: Replaces sensitive payment card data with a unique, non-sensitive identifier (a “token”). This token can be used for transactions, but it’s meaningless if intercepted, protecting the actual card details.
- Encryption: Scrambles sensitive data during transmission and storage, making it unreadable to unauthorized parties.
6. Strong Customer Authentication (SCA)
For merchants operating in Europe, SCA, mandated by PSD2 (Revised Payment Services Directive), requires multi-factor authentication for most online transactions. This typically involves two out of three elements: something the customer knows (e.g., password), something the customer has (e.g., phone with an OTP), and something the customer is (e.g., fingerprint, facial recognition).
7. Fraud Scoring
Many fraud prevention systems assign a “fraud score” to each transaction based on various risk factors. Merchants can set thresholds to automatically approve, deny, or flag transactions for manual review based on these scores.
8. Blacklists and Whitelists
- Blacklists: Maintain lists of known fraudulent IP addresses, email addresses, card numbers, or customer accounts to automatically block transactions.
- Whitelists: Maintain lists of trusted customers or IP addresses to streamline their transactions.
9. Customer Education
Educate customers on how to protect themselves from phishing, create strong passwords, and recognize secure websites. A well-informed customer base is an additional layer of defense.
10. Robust Chargeback Management
Even with strong prevention, some chargebacks are inevitable. Merchants need a clear process for responding to chargebacks, gathering compelling evidence (proof of delivery, customer communication, AVS/CVV matches) to dispute illegitimate claims, especially “friendly fraud.”
For Cardholders
While merchants and banks bear much of the responsibility, cardholders also play a crucial role in protecting themselves from CNP fraud.
- Monitor Bank and Credit Card Statements Regularly: Check for any unauthorized or suspicious transactions, even small ones. Report them immediately to your bank or card issuer.
- Use Strong, Unique Passwords and Two-Factor Authentication (2FA): For all online accounts, especially those linked to payment information. 2FA adds an extra layer of security, making it much harder for fraudsters to access accounts even if they have your password.
- Shop on Secure Websites (HTTPS): Always look for “https://” in the website address and a padlock icon in the browser bar before entering any payment information.
- Be Wary of Phishing and Smishing Scams: Never click on suspicious links in emails or text messages, and never provide personal or financial information in response to unsolicited requests.
- Report Lost or Stolen Cards Immediately: The sooner you report a compromise, the faster your bank can block the card and prevent fraudulent use.
- Consider Using Virtual Card Numbers: Some banks offer virtual card numbers that are temporary, single-use, or merchant-specific, adding an extra layer of protection by not exposing your actual card number.
- Be Cautious with Public Wi-Fi: Avoid making online purchases or accessing sensitive accounts when connected to unsecured public Wi-Fi networks, as these can be vulnerable to eavesdropping.
The Future of CNP Fraud Prevention
As fraudsters continue to innovate, so too must prevention strategies. The future of CNP fraud prevention will likely involve:
- Even More Advanced AI and Machine Learning: Real-time, adaptive AI systems will become even more sophisticated, capable of detecting subtle anomalies and predicting fraud with greater accuracy, learning from new attack vectors instantly.
- Biometric Authentication: Wider adoption of biometrics like fingerprint scanning, facial recognition, and voice recognition for payment authorization, especially on mobile devices, offering a more secure and convenient authentication method.
- Behavioral Biometrics: Analyzing unique user behaviors like typing rhythm, mouse movements, and swipe patterns to verify identity without explicit user input, providing a seamless yet secure experience.
- Blockchain Technology: While still nascent in payments, blockchain could offer immutable and transparent transaction records, potentially enhancing security and traceability, though scalability and integration remain challenges.
- Enhanced Data Sharing and Collaboration: Greater collaboration between financial institutions, merchants, payment processors, and law enforcement to share threat intelligence and best practices, creating a collective defense against organized fraud rings.
- Contextual Authentication: Moving beyond static authentication to dynamic, risk-based authentication that considers the context of each transaction (e.g., device, location, purchase history) to determine the appropriate level of security challenge.
These innovations aim to create a more secure and frictionless payment experience, making it increasingly